Category: Security
-

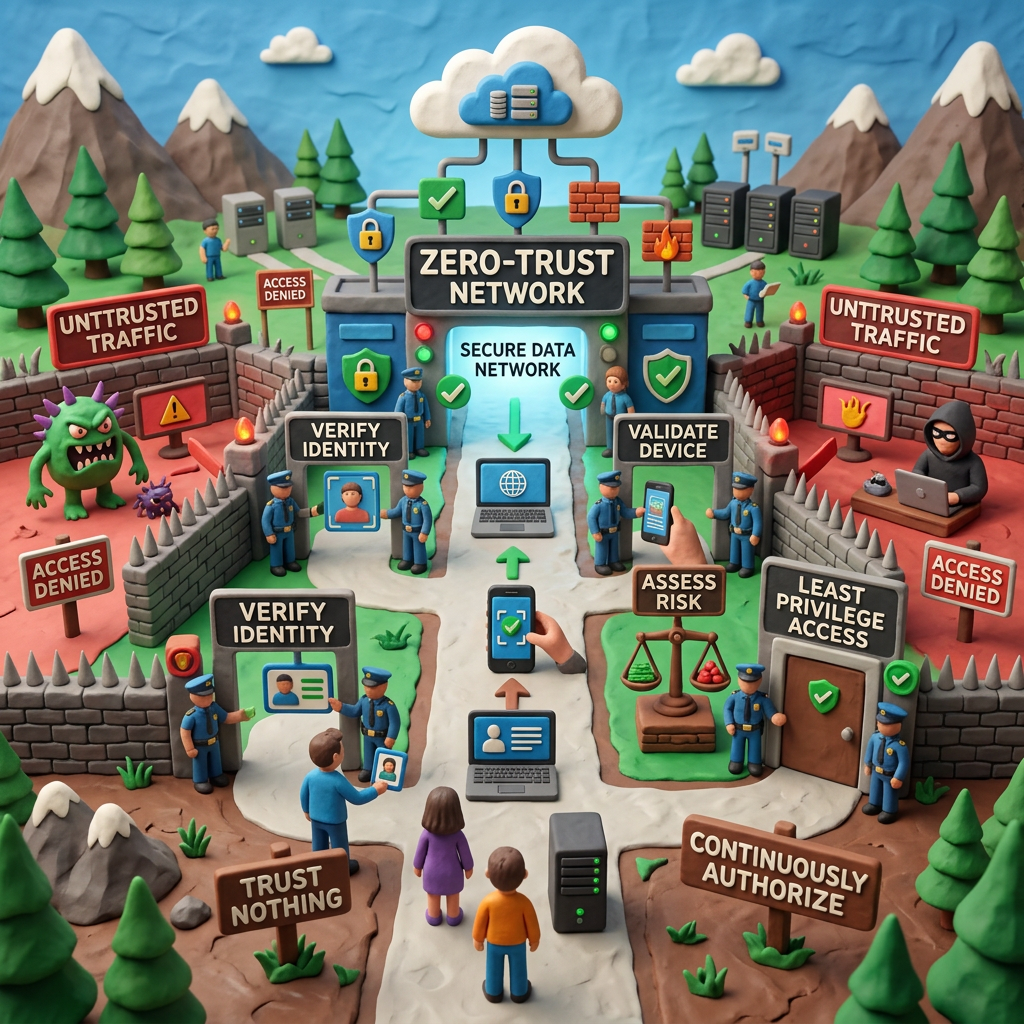
Identity is the cornerstone of Zero Trust, and for those who don’t know, identities are not just user accounts, they’re devices and service principles also. For this blog post I will focus on how I apply Zero-trust Principles on clients Entra ID environments. Before I dive into this, let’s have a look at the Zero-trust…
-
Anyone who has deployed WHfB would know there are multiple deployment methods depending on the org setup and the device management state (Hybrid, On-Prem, Cloud). I’ll discuss three deployment methods using Intune for devices registered in Active Directory and synced to Entra, and for cloud only Entra joined devices. Here are the three WHfB deployment…
-
Endpoint Privilege Management allows end-users to elevate applications in a controlled manner, thus reducing the requirement for standard user’s requiring local admin permissions to install executables, upgrade applications, etc. In this blog post, I’ll show you a phased approach to deploying EPM and then show you how I like to deploy EPM while following a…